Compliance files go stale. Our system keeps yours current.
Your appointments, registers, certificates and evidence stay live between audits, not just on the day one is done. Run to the Act and the regulations, remote by design, anywhere in South Africa.
GRC Shop gives South African businesses one central operating layer for compliance. Activate the APP that fits your needs now, then expand over time without rebuilding the record, workflows or visibility. Software handles the tracking, reminders and paperwork; qualified people own the review and sign-off.
B-BBEE Exempt Micro Enterprise (EME) · Reg. 2025/768856/07
Talk to us about your OHS compliance
Tell us where you are exposed and we will come back to you within two business days. No obligation.
What GRC Shop does
GRC Shop is an outsourced occupational health and safety compliance service for South African employers. We take on your duties under the Occupational Health and Safety Act 85 of 1993: statutory appointments and their letters, the registers you are required to keep, certificate and expiry tracking, incident reporting timelines, and the evidence an inspector asks to see.
The work is done remotely and supervised, and every appointment and register is traced to the section or regulation that requires it. You get an app you can log into, so the current state of your compliance is visible rather than sitting in someone else’s filing cabinet.
Occupational health and safety is the only service available today. POPIA, labour, CIPC, SARS and FICA are on the roadmap and are not services you can buy from us yet. The checklists we publish for those areas are free guides, not products.
How you can check us before you commit
We are a young firm, so rather than ask you to take our word for it, here is work you can inspect yourself right now.
Every requirement is sourced
Our published OHS Inspection Register carries 52 citations to sections of the Occupational Health and Safety Act and 74 to its regulations. Where a figure is our operating practice rather than an explicit legal ratio, the page says so instead of presenting it as law.
We publish our corrections
When we get something wrong we correct it in public and date it, rather than quietly editing the page. Our most recent published correction is dated 25 August 2026.
The site is tested, not assumed
Automated WCAG 2.1 AA testing with axe-core on 30 August 2026 returned zero violations on our OHS service page, the inspection register and the FAQ. Automated testing does not catch everything, so we say what was measured and when.
What you actually see
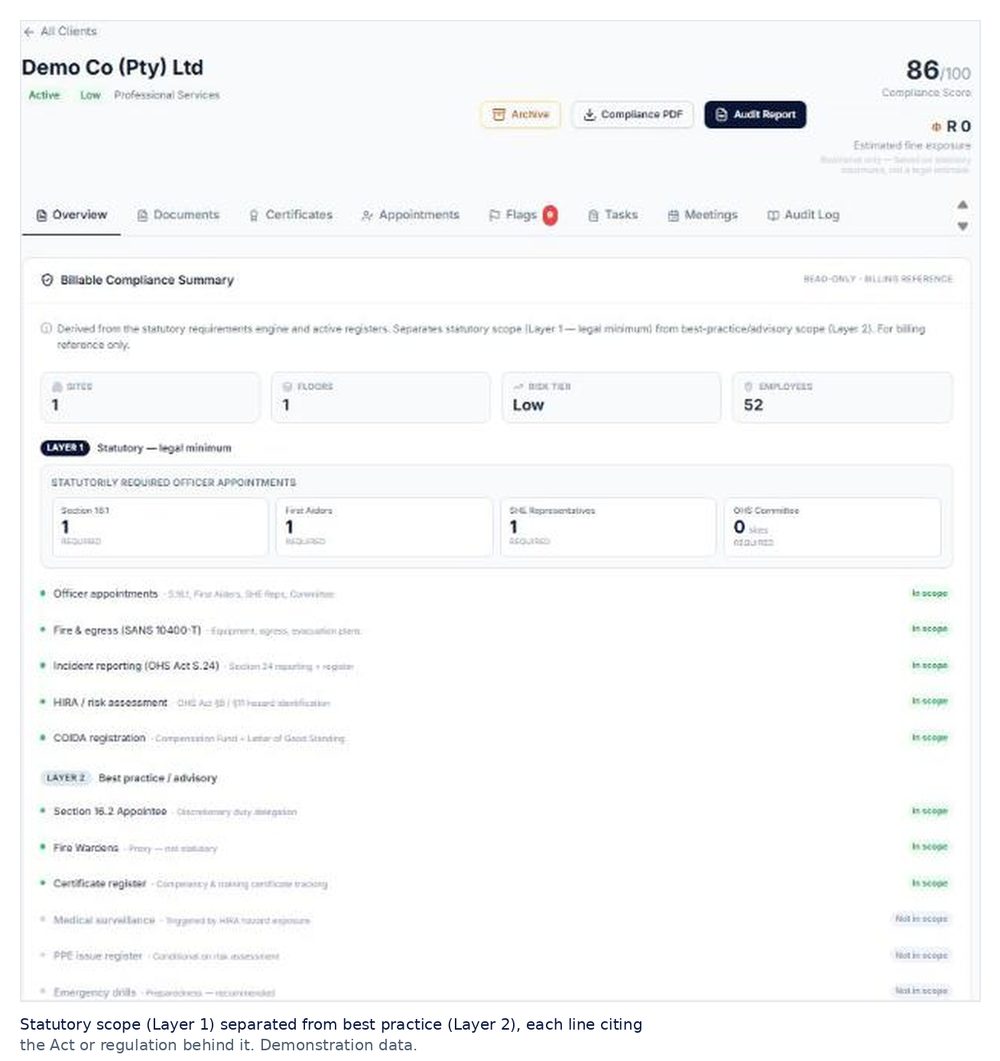
Every requirement we track is separated into what the law requires and what is good practice, with the section or regulation named beside it. Nothing is asserted without a source.
Live record
One managed operating layer keeps obligations, workflows, evidence and visibility current.
One App per Domain
Start with one compliance domain, then add more APPs without rebuilding the model.
Continuous oversight
Internal changes, specialist input and regulatory updates keep the record live over time.
Centralised and live
One live compliance record replaces fragmented files, scattered updates and version confusion.
Continuous oversight
Reviews, actions, renewals and follow-through stay active after the first setup.
Remote model built to scale
National reach, tighter turnaround and less cost drag than visit-heavy delivery models.
Controlled cost and control
Clients keep visibility and approvals without carrying the full admin burden internally.
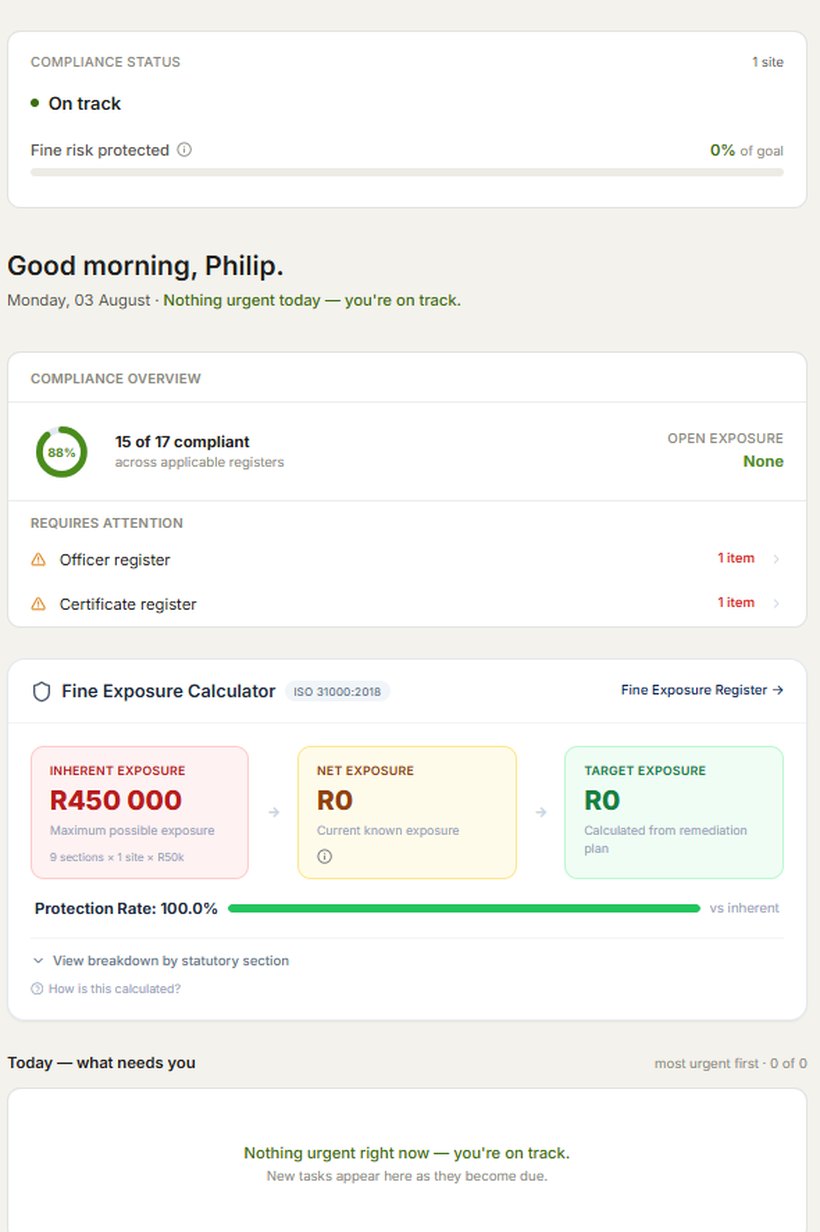
What clients see every day: live compliance status, fine-risk exposure and exactly what needs attention.
One operating layer for compliance
Centralise records, actions, evidence and approvals in one managed environment. The platform keeps every active APP connected so the compliance record stays visible and current.
The Platform is not just where you start. It is the integration layer that connects every APP you add. One record. One place. No disconnected systems.
Central record
It keeps the compliance record live across documents, actions, evidence, permissions, reviews and renewals, not just at setup but continuously.
APP-based domains
Each APP covers one compliance domain with its own workflows, documents and obligations, all running inside the same managed environment.
Explore the compliance apps: OHS · POPIA · Labour · FICA / AML · CIPC · SARS
Client control
Client approvals stay where needed. Outside advisors can contribute when needed. The master record still stays centralised and visible.
Traditional models fragment ownership
Files, updates and responsibilities get split across email threads, folders, consultants and internal teams.
Updates get lost between events
Injuries, appointments, renewals, staffing changes and regulatory updates keep moving, even when the documentation pack is already "done".
Many businesses lack in-house capacity
Most businesses do not have the time, systems or specialist coordination needed to keep compliance current on an ongoing basis.
Remote by design. Built to stay active.
GRC Shop is delivered remotely by design so the service can respond faster, keep process control tighter and support clients across South Africa without travel drag.
National reach without travel drag
More clients, more consistency, less time lost to logistics and scheduling friction.
Structured records beat ad-hoc files
The operating system becomes the source of truth, and documents are outputs of that system.
Better unit economics
The model scales by process, product and platform, not only by adding more consultants.
Questions before you start
What you can check before you talk to us
We are early and we would rather be checkable than impressive. Everything below is either published on this site or verifiable independently, so you can form a view without taking our word for anything.
The OHS service is live, not a demo
The occupational health and safety app is in service and carrying real statutory obligations. The screenshots on this site are the actual client portal, not mockups: the modelled fine exposure position, the compliance status, the appointment letters and the registers.
See what it managesOur workings are published, with the section behind them
Five free compliance checklists covering POPIA, Labour, FICA, CIPC and SARS, plus an OHS Act guide. Every item carries the section of the Act or the regulation it comes from, so you can check us against the primary source rather than against our confidence.
Read the checklistsWe publish where the market gets it wrong
The widely repeated ratio of one health and safety representative per 20 employees is not what the Act says. We set out the correct position, with the subsection, because a provider who repeats the market version will compute your shortfall wrongly.
See the thresholdsOur own compliance is on the table
02X (Pty) Ltd t/a GRC Shop, registration 2025/768856/07, verifiable at CIPC. Our PAIA manual, our public POPIA policy and our B-BBEE Exempt Micro Enterprise certificate are all published and downloadable, not available on request.
Read the PAIA manualA named person signs off
Software handles the tracking, the reminders and the paperwork. A qualified person owns the review and the sign-off, and that person is named, with credentials you can verify against the professional bodies that issued them.
Who signs off, and the credentials behind itWe say what stays with you
We surface the obligation, the evidence and the gap. You decide on remediation and you remain the party the regulator holds responsible, because that is how the statutes are written and no service agreement changes it. Anyone promising otherwise is overselling.
How the split worksProfessional indemnity cover is in place
We carry professional indemnity insurance for the compliance work we do. Written confirmation of cover is available on request, and we confirm it in writing before any engagement starts.
Why there are no testimonials on this page. Our client relationships are confidential, and we will not publish a quote we do not have written consent for, or one we wrote ourselves. When a client is willing to be named and quoted, their words will appear here and nobody else’s will. In the meantime, the checkable things above are a better basis for a decision than a paragraph in quotation marks.
Our own record
Method metrics, not client outcomes
We will not publish an aggregate drawn from a single client, so instead we publish what can be checked about how we work. Every number below is verifiable on this website without asking us for anything.
Cited in our public OHS inspection register, each item anchored to the provision behind it rather than asserted.
Automated WCAG 2.1 AA testing on the pages we audit, re-run after every material change. Automated testing catches part of the picture, so this is a floor and not a certificate.
We had a statutory detail wrong. We corrected it in the register, in the guide that repeated it and in the diagram that illustrated it, and we said so in writing instead of editing quietly.
The response commitment on every enquiry from this website, stated the same way on every page that carries a form.
What is deliberately not here: client counts, hours saved and percentage improvements. We have one external client onboarding and no permission to name them, so any aggregate would mislead you. When there is a client outcome to publish, it will carry a name and a number.
WHO STANDS BEHIND YOUR COMPLIANCE
Named people, not a faceless app
GRC Shop is run by 02X (Pty) Ltd, a registered South African company. Qualified people build the work, review it, and sign it off. Software handles the tracking, reminders and paperwork; people own the accountability.
Registered company
02X (Pty) Ltd t/a GRC Shop. Registration 2025/768856/07. B-BBEE Exempt Micro Enterprise.
Qualified sign-off
Founder Philip de Witt: Chartered Management Accountant (ACMA, CGMA), MBA from the UCT Graduate School of Business, and an ISO 45001:2018 occupational health and safety qualification from the SABS.
Chartered finance and governance
A CA(SA) chartered accountant on our team keeps the financial and governance controls sound.
POPIA and PAIA
Your information is handled under POPIA, and our PAIA manual is published and available on request.
Qualified people own the review and sign-off on the compliance work we produce for you. Meet the founder.
Get started with the right setup
Tell us where the biggest compliance pressure is right now. We will review the context, share your Platform link, and guide you to the APP or APPs that fit your business, location and risk profile.